Harvard University reveals data breach exposed 851,000 accounts

Harvard breach data affecting 850,500 people has now surfaced in breach-tracking databases and dark web archives Exposed information includes emails, contact details, demographics, and extensive alumni and donor profile data Attack highlights ongoing…
Hackers exploited iOS and Android flaws to infect phones

Hackers possibly linked to the Kremlin exploited previously patched iOS and Android flaws in an attempt to hack visitors of multiple websites, including one celebrating the 250th anniversary of the signing of the US Constitution, researchers said…
Researchers warned of North Korean hacking tactics years before record $6.3B Binance heist

Cybersecurity experts have long warned of the persistent and patient threat from North Korea’s long-running hacks. The world’s largest crypto exchange was still caught off-guard.Go to story
Hackers stole DreamHost customer files and inboxes during months-long attack
The web host said hackers exploited a vulnerability to access customer emails and files during a “deliberate attack.”Go to story
Hacker steals millions by scamming high-stakes online poker games with this devious malware attack
Malware allegedly gave a poker cheat access to opponents’ computer screens Hundreds of online poker players may have suffered financial losses MeshAgent reportedly helped the attacker monitor selected players during games Online poker players are…
Binance Says Hackers Used Well-Known Tricks to Carry Out a $6.34 Billion Heist

Suspected North Korean attackers duped an engineer with a fake job interview and a malicious download to gain a foothold in the crypto firm’s system and steal billions, according to Binance.Go to story
Hugging Face’s CEO Says His P(Doom) Is ‘Close to Zero’
“Most of the risk is actually created by a couple of players building behind closed doors,” Clément Delangue said of the need for open source AI.Go to story
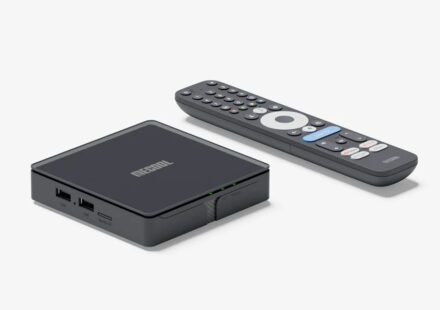
Google dismantles botnet secretly running on 1.3 million Android TV boxes
Google’s Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed…
UEFI bootkit infected fully patched Windows machines. Is Microsoft to blame?
In 2023, malware tracked as BlackLotus became the first publicly documented in-the-wild UEFI bootkit capable of bypassing Secure Boot on fully updated Windows 11 systems. With the industry-wide chain-of-trust mechanism subverted, the malware was able to…
Singapore Airlines says 46,000 booking records hit following Amadeus breach
Singapore Airlines confirms customer data exposure through a breach at travel technology provider Amadeus Stolen booking records included passenger details, itineraries, and limited passport and loyalty-program information Multiple major airlines were…